CLEAR 2026:55. The new IT standard.
55 controls covering both halves of what auditors check: the settings, and the program around them. Every SOC 2 and ISO 27001 requirement maps to one of them.
Domain and website
3
Who controls your domain, your DNS records, your website's secure connection
3
Admin access, fake email blocked, hidden forwarding rules
Files and sharing
2
Your shared drives, and who can open what
Network, Wi-Fi and remote access
4
Your office network, Wi-Fi, web filtering, safe remote access
Passwords and sign-in
4
Password manager, strong passwords, two-step sign-in for everyone
Computers and phones
6
Encryption, device management, threat protection, wiping old devices
Updates, monitoring and weak spots
6
Alerts, logs kept, updates on schedule, known holes patched
Your office
4
Locked equipment, cameras where they matter, fire and power, visitors
Backups and recovery
4
A real backup, tested restores, a plan for getting back to work
Your team
5
Training, practice phishing, offboarding, background checks
When something goes wrong
4
How staff report it, the response plan, written policies, roles
Cloud apps and vendors
4
Every app you pay for, who has access, how safe your vendors are
Privacy and compliance
4
The rules that apply to you, personal data, breach notices
Payments and the yearly review
2
Two-person approval for payments, a yearly review you sign
Your checklist, by area
Every control and where it stands, in your portal.
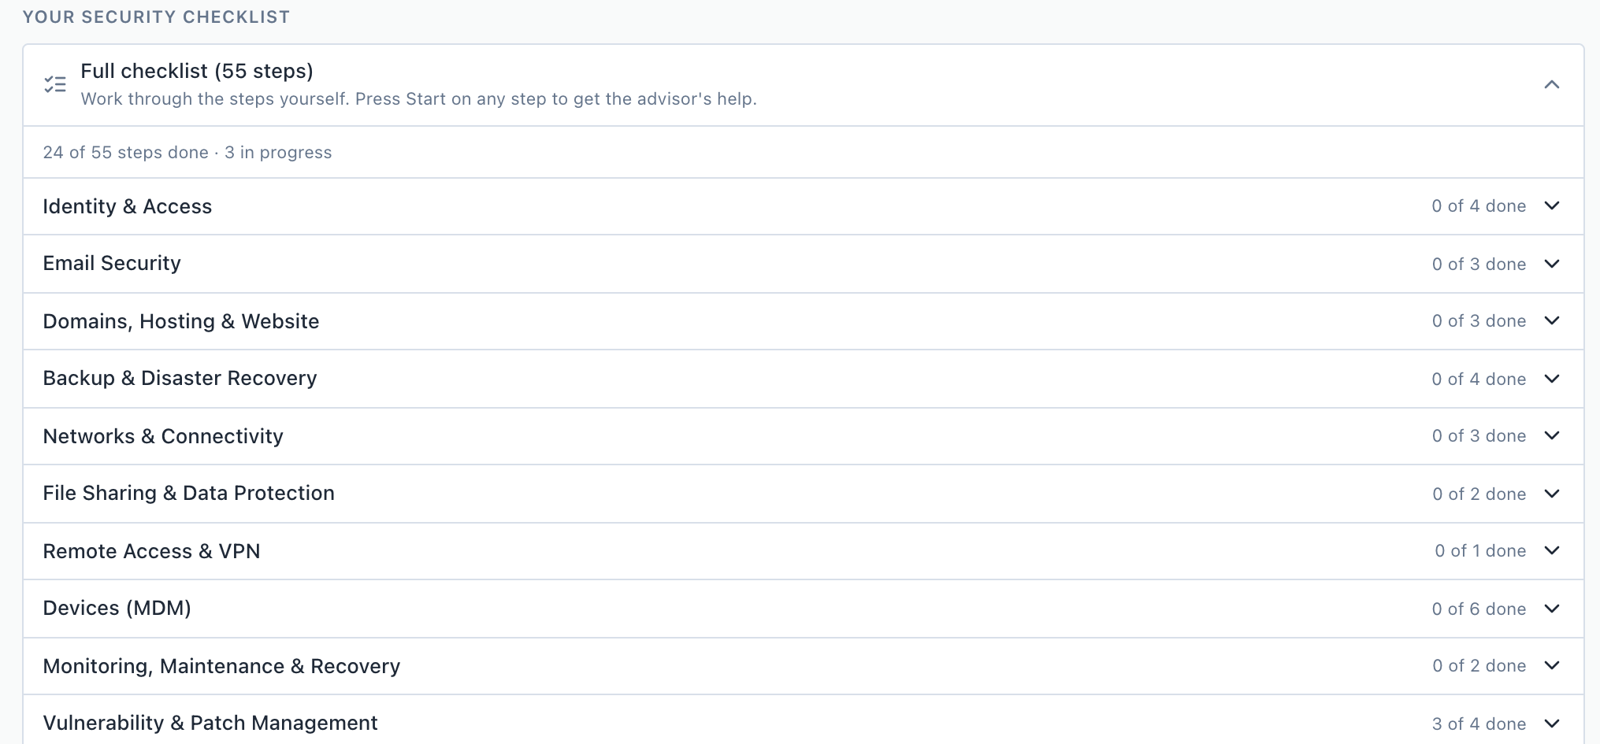
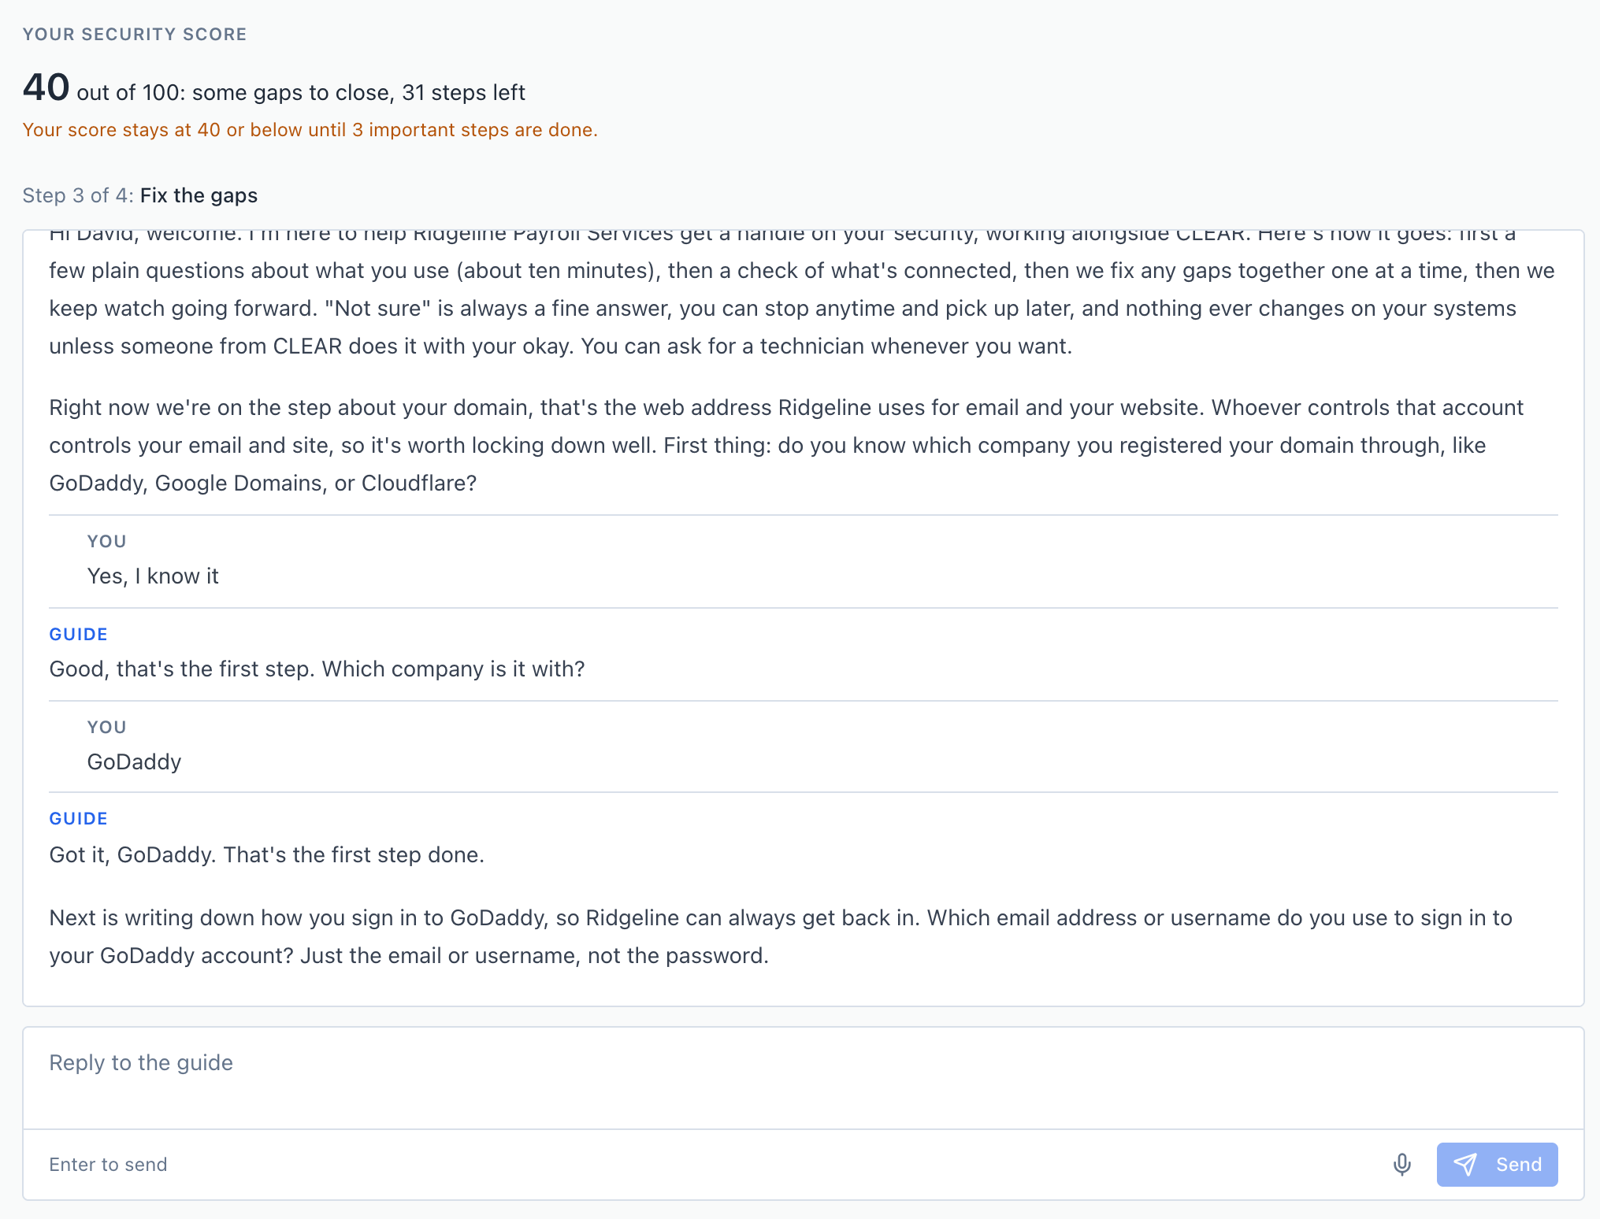
An honest note. CLEAR 2026:55 is our own standard. Only an audit firm can issue a SOC 2 report, and only an accredited body can certify you for ISO 27001. What you get from us is everything those audits check, except the controls for writing software, with the evidence behind each item. If you decide to get certified, your auditor starts from our record instead of a blank page.
Security your insurer can sign off on.
See all 55 controlsThe standard
CLEAR 2026:55: 55 controls, and every SOC 2 and ISO 27001 requirement maps to one of them.
Access
Two-step sign-in on every account. Passwords are stored encrypted, and every view is logged.
Privacy
WarpMSP reads how a computer is doing, never your files, email or browsing. Remote sessions need your OK and are never recorded.
Proof
A person approves every change, and every change goes on your record for an insurer, customer or auditor.
CLEAR 2026:55 is our own standard. Only an audit firm can issue a SOC 2 report, and only an accredited body can certify you for ISO 27001. What you get from us is everything those audits check, with the evidence behind each item.
See where you stand.
Type your company's website address. We'll show you what anyone on the internet can see, and fix the two worst things free.